Resend Transactional Email in Next.js
A practical resend transactional email guide for Next.js: domain setup, server-side sending, errors, testing, and launch checklist.
Build My App Fast · Sep 19, 2026 · 10 min read
resend transactional email in Next.js means one thing in production: send the email from trusted server code after the important database or payment event succeeds. The basic API call is simple. The real work is choosing the right trigger point, keeping API keys out of the browser, handling failures, and making sure users do not get duplicate or missing emails.
At Build My App Fast, Resend is one of the tools we use often in Next.js, Supabase, Stripe, Tailwind, Resend, and Vercel builds because it is fast to wire into a real app without adding a heavy email platform. This guide shows the practical setup we would use for welcome emails, invites, receipts, waitlist confirmations, and other transactional messages.
Why transactional email is different from marketing email
Transactional email is tied to a user action or account event. It is not a newsletter. It is not a drip campaign. It is the email your app sends because something happened.
Common examples:
- Welcome email after account creation
- Email verification or password reset flow
- Team invitation email
- Receipt or subscription status email
- Waitlist confirmation
- Support request confirmation
- File export ready notification
- Admin alert for a high-value action
That distinction matters because transactional email is part of the product experience. If the email fails, the user may be blocked. If it sends twice, the product feels sloppy. If it leaks internal data, you have a security issue.
This is why email belongs in the same production checklist as auth, payments, database rules, and deployment. If you are moving quickly, use a launch checklist like Vibe Code to Production Checklist instead of treating email as a last-minute polish task.
resend transactional email setup in Next.js
The core setup is straightforward: create a Resend account, verify a sending domain, add an API key to your environment variables, install the SDK, and call it from server-side code.
Use the official Resend documentation for current dashboard steps, domain verification, and SDK details. For the Next.js side, route handlers are documented in the official Next.js Route Handlers docs.
Here is the production-oriented version of the setup:
| Step | What to do | Production note |
|---|---|---|
| Verify domain | Add the DNS records Resend gives you | Do not launch from a temporary sender if users need to trust the app |
| Add API key | Store it as RESEND_API_KEY | Never expose it with NEXT_PUBLIC_ |
| Create sender | Use a real product address like hello@yourdomain.com | Keep support and system senders consistent |
| Write server helper | Put the Resend call in a reusable server-only function | Avoid copying email calls across routes |
| Trigger after success | Send after DB write, auth event, or payment confirmation | Do not send before the source-of-truth event succeeds |
| Log failures | Capture the error and event context | Do not silently swallow failed product emails |
Install the package:
npm install resend
Add your environment variable locally:
RESEND_API_KEY=re_your_key_here
Then add the same variable in your hosting provider. On Vercel, that means Project Settings, Environment Variables, and redeploying after the value is added. This is one of the deployment details founders often miss; we cover the broader deployment picture in Deploy Next.js Vercel: What Founders Need to Know.
Create a server-side email helper
Do not call Resend directly from a React client component. Your API key belongs on the server. A simple helper keeps your app organized and makes it easier to change templates later.
Example file: lib/email/send-welcome-email.ts
import { Resend } from 'resend';

const resend = new Resend(process.env.RESEND_API_KEY);

type SendWelcomeEmailInput = {
  to: string;
  name?: string;
};

export async function sendWelcomeEmail({ to, name }: SendWelcomeEmailInput) {
  if (!process.env.RESEND_API_KEY) {
    throw new Error('Missing RESEND_API_KEY');
  }

  const { data, error } = await resend.emails.send({
    from: 'Your App <hello@yourdomain.com>',
    to,
    subject: 'Welcome to Your App',
    text: `Hi ${name ?? 'there'}, your account is ready.`,
  });

  if (error) {
    throw new Error(error.message);
  }

  return data;
}
For many MVPs, a plain text email is enough. HTML templates are useful, but they are not the first problem to solve. The first problem is reliable delivery at the right moment.
If you do add HTML, keep it boring: clear subject, clear sender, one primary action, and a plain text fallback. Transactional email is not the place for clever layouts that break in half of the inboxes your users open.
Call Resend after the product event succeeds
The biggest mistake is sending the email too early.
If a user signs up, write the user record first. If a customer pays, confirm the Stripe event first. If someone submits a contact form, validate and store the submission before sending the confirmation.
A simplified route handler might look like this:
import { sendWelcomeEmail } from '@/lib/email/send-welcome-email';

export async function POST(request: Request) {
  const body = await request.json();

  // Validate input here.
  // Create the user or write the database record here.

  await sendWelcomeEmail({
    to: body.email,
    name: body.name,
  });

  return Response.json({ ok: true });
}
That example is intentionally short. In a production app, we would also validate the input, authenticate the request if needed, record the event, and decide what should happen if Resend returns an error.
For Stripe subscription apps, the safest pattern is usually to send email from webhook-confirmed events, not from optimistic checkout UI state. If you are adding billing to a Next.js app, read Stripe Next.js Payments: 2026 Guide before deciding where receipt, trial, and cancellation emails should be triggered.
Avoid duplicate emails
Duplicate email is one of the most common production bugs in early SaaS apps. It usually comes from retries, double form submissions, webhook replays, or code that sends from both the frontend success page and the backend handler.
The fix is not just debounce on the button. You need an idempotent product event.
For example, instead of saying send invite email whenever this endpoint is called, model the action as an invite record:
- Create invite with status pending
- Store inviter, invitee email, organization, and token
- Send the invite email once
- Record sent_at or resend_message_id
- If the endpoint is retried, check the existing invite before sending again
This pattern matters more as soon as you have teams, billing, approvals, or admin workflows. Email should reflect your database state, not the other way around.
If your app uses Supabase, row-level security and server-side policies also matter. Email links often reveal resources such as invites, organizations, or private dashboards. Pair this guide with Supabase Row Level Security, Explained Simply if users should only access records they are allowed to see.
What to log when Resend fails
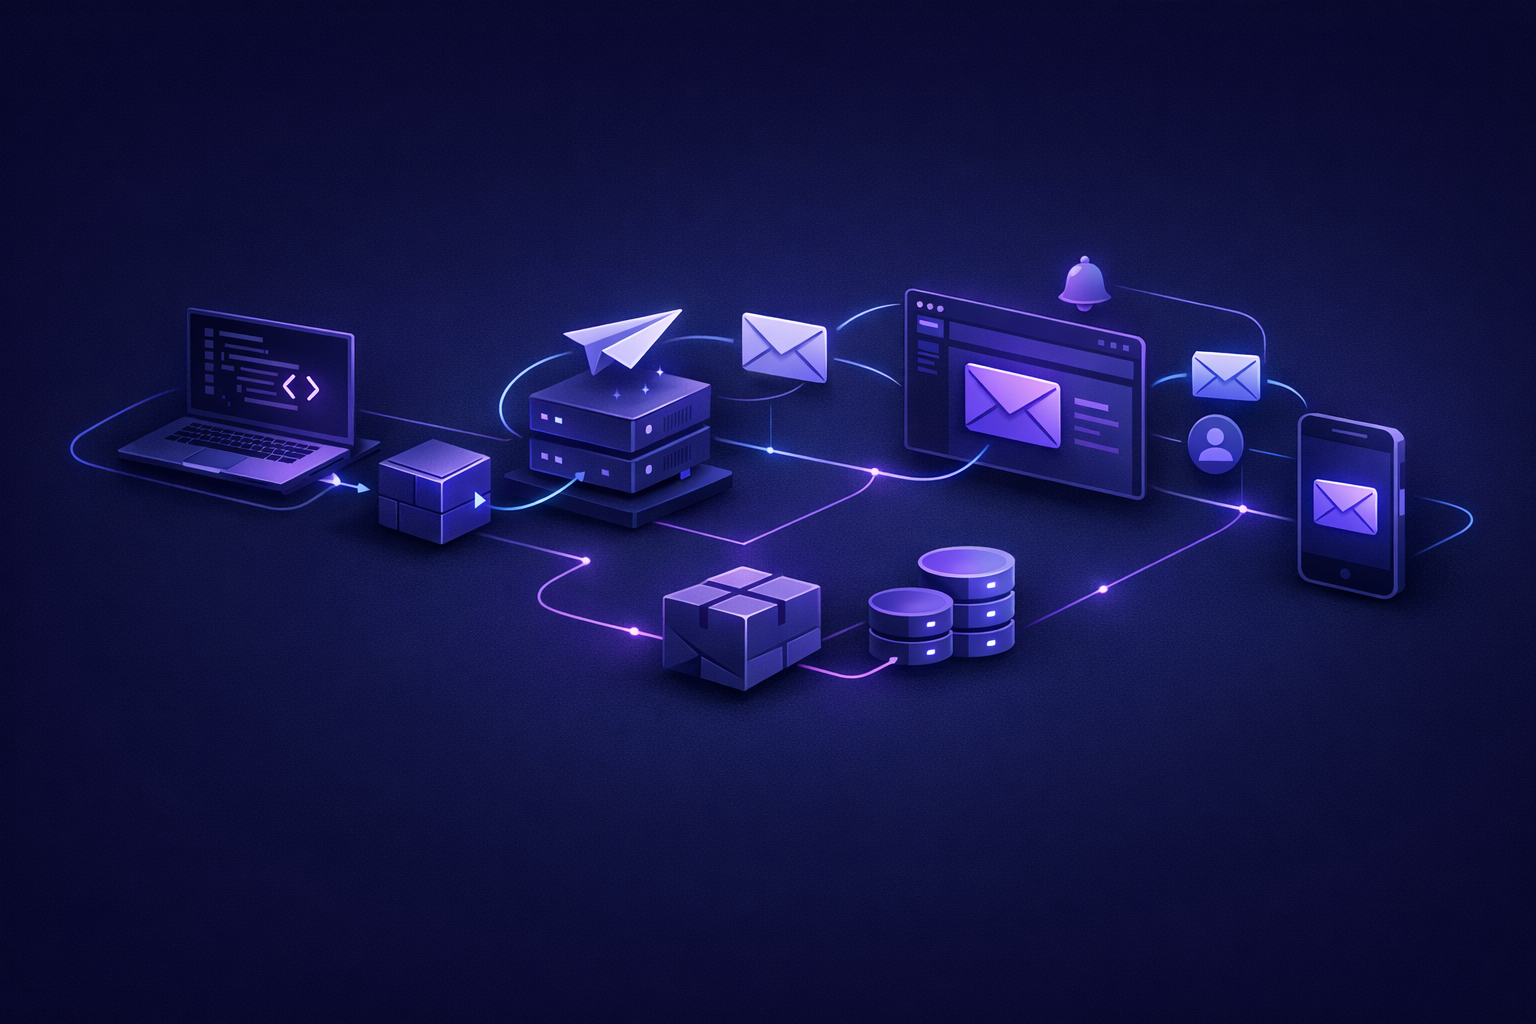
A production app should not fail silently when transactional email fails. At the same time, not every email failure should break the user experience.
Use judgment:
- If a password reset email fails, return a safe message and log the failure.
- If a receipt email fails after payment succeeds, do not undo the payment. Log and retry manually or through a job.
- If a team invite email fails, show an admin-visible error so the inviter can try again.
- If an internal notification fails, keep the user flow moving and alert the team separately.
At minimum, log:
- Email type
- Recipient email
- Related user or account ID
- Related payment, invite, or form ID
- Resend response error
- Timestamp
Do not log secrets, magic login links, reset tokens, or full private message bodies. Logs are part of your security surface.
Testing resend transactional email before launch
Email needs a real test path, not just one happy-path send from a local machine.
Use this checklist before launch:
- Sending domain is verified
- Production environment has RESEND_API_KEY set
- Local, preview, and production environments use the right sender
- API key is not exposed to the client bundle
- Email sends only after the database or payment event succeeds
- Duplicate form submissions do not send duplicate emails
- Failed sends are logged with enough context
- Templates include plain text or readable fallback content
- Reply-to address goes somewhere monitored
- Unsubscribe handling is considered if the email is not purely transactional
For a pre-launch waitlist, email is especially important. The first message sets expectations and can drive the next action, such as booking a call, joining a beta, or confirming interest. We break down that funnel in Pre Launch Waitlist: How to Actually Convert.
How this fits into a fast MVP build
Transactional email should not turn into a custom notification platform during an MVP. The right scope depends on the stage.
For a $1,000 Proof of concept delivered in 2–4 days, email might be one confirmation message or one admin notification if it helps validate the workflow.
For a $5,000 Real app delivered in 4–6 days, email usually supports real accounts, a database-backed workflow, and basic operational messages such as invites, confirmations, or support notifications.
For a $10,000 Launchable MVP delivered in 7–10 days, email may connect to subscriptions, integrations, or AI features. That is where webhook-driven messages, retry behavior, and event logs become more important.
The principle is the same at every tier: ship the smallest email system that supports the product promise, not a bloated notification center.
Common Next.js and Resend mistakes
Here are the issues we watch for when reviewing early codebases:
- API key in client code. If the file starts with use client, it should not import Resend or read the secret key.
- Sending before persistence. If the database write fails after the email sends, the user receives a message about something that does not exist.
- No idempotency. Retries, reloads, and webhook replays can all send duplicates.
- Hardcoded production recipients. Test emails accidentally go to real users because staging and production are not separated.
- From address mismatch. The sender in code does not match the verified domain or product identity.
- Treating email as proof of state. The database should be the source of truth, not the inbox.
- No operational visibility. If a founder asks whether an invite sent, the team has no answer.
Most of these are not Resend problems. They are application architecture problems. Resend handles sending. Your app still owns timing, state, permissions, and recovery.
FAQ
Should I send Resend emails from a Server Action or Route Handler?
Either can work. Use a Server Action when the email belongs directly to a trusted server-side form action. Use a Route Handler when the trigger comes from a webhook, external integration, mobile client, or explicit API endpoint. The important rule is the same: keep the Resend API key server-side.
Can I use Resend for auth emails with Supabase?
Yes, but decide where auth email responsibility lives. Supabase Auth can handle standard auth flows, while your app can use Resend for product emails such as onboarding, team invites, and billing notifications. Avoid two systems sending overlapping account messages.
Do I need HTML email templates for an MVP?
Usually not at first. A clear plain text email with the right subject and link is often better than a fragile template. Add branded HTML once the workflow is proven and the email content is stable.
What happens if Resend is temporarily unavailable?
Your app should handle the error based on the email type. Some flows should show a retry option. Others should log the failure and let the core product event remain successful. For critical workflows, store an email event record so you can retry without duplicating the underlying action.
Need this wired into a real Next.js MVP with auth, database, payments, and production deployment? Apply to Build My App Fast.